Ransomware detection is not a single product setting or one alert in a security dashboard. It is a repeatable process for recognizing suspicious activity, confirming what it means, containing risk, and recovering without creating additional damage. A practical approach to Cohesity ransomware detection starts by connecting signals from people, identities, devices, networks, data, and backups.
The objective is not to treat every unusual event as a confirmed attack. It is to make sure meaningful warning signs receive fast, informed attention before an intruder can move through the environment, encrypt data, disrupt operations, or interfere with recovery systems.
Why Speed Matters During a Ransomware Attack
The first minutes and hours of an incident can shape the eventual business impact. An attacker who gains access through a compromised account may spend time identifying valuable systems, changing permissions, disabling defenses, or reaching shared storage before encryption begins. A fast review gives teams a chance to isolate affected accounts or devices while the scope is still manageable.
Consider an employee account that begins accessing unfamiliar folders overnight, creates large numbers of files, and attempts connections to systems it has never used. Any one event might have an innocent explanation. Taken together, the pattern should trigger immediate investigation.
Early Signals That Deserve Attention
Detection improves when teams look for related behavior instead of evaluating every event in isolation. Useful warning signs often include:
- Rapid file creation, deletion, renaming, or extension changes.
- Repeated failed logins followed by a successful sign-in.
- Access from an unfamiliar device, location, or time of day.
- Unexpected administrator accounts or privilege changes.
- Security software settings are being disabled or altered.
- Unapproved use of remote administration tools.
- Large transfers of data to unfamiliar destinations.
- Backup jobs that fail, stop, or change without authorization.
Context matters. A large transfer may be routine for a design team moving media files, but unusual for a finance workstation. Establishing normal patterns for users, systems, and departments makes meaningful deviations easier to identify.
The Main Layers of Ransomware Detection
Known Indicators and Signatures
Security tools can identify known malicious files, domains, hashes, and other indicators. These controls remain useful, but they may not recognize newly modified malware or activity performed with legitimate credentials and administrative tools.
Behavior-Based Detection
Behavioral analytics focuses on actions that do not fit an expected pattern, such as rapid encryption-like file activity, unusual lateral movement, or a sudden effort to change backup settings. This approach can help uncover suspicious activity even when the exact malware family is unknown.
Threat Intelligence and Deception
Current defensive guidance can help organizations align monitoring and response practices with common attack paths. The ransomware prevention and response guidance published by CISA emphasizes preparation, detection, containment, and recovery. Canary files, monitored decoy accounts, and other deception controls can add high-value signals when an unauthorized process or user interacts with resources that normal work should never touch.
How Identity and Access Fit Into Detection
Ransomware detection should extend beyond endpoints and file servers. Attackers may use stolen credentials, remote access services, or compromised administrator accounts to appear legitimate. Monitoring identity activity helps teams recognize access that is valid on paper but suspicious in context.
- Require multi-factor authentication for important systems.
- Review privileged accounts and remove unused access.
- Alert on unusual login patterns and impossible travel scenarios.
- Limit administrative rights on everyday user accounts.
- Record access to sensitive systems and shared storage.
Watching Data Behavior Without Creating Alert Noise
Data monitoring should begin with a baseline. Track normal file operations, storage activity, database exports, cloud downloads, and backup schedules before setting aggressive thresholds. Then group related alerts by user, device, data source, and time window so analysts can assess the full story rather than chase disconnected notifications.
Priority monitoring areas include rapid file modifications, permission changes, unusual after-hours access, unexpected database exports, and changes to recovery infrastructure. Alert tuning is ongoing work. Rules that are too broad can overwhelm analysts, while rules that are too narrow can miss meaningful behavior.
A Simple Detection-to-Response Workflow
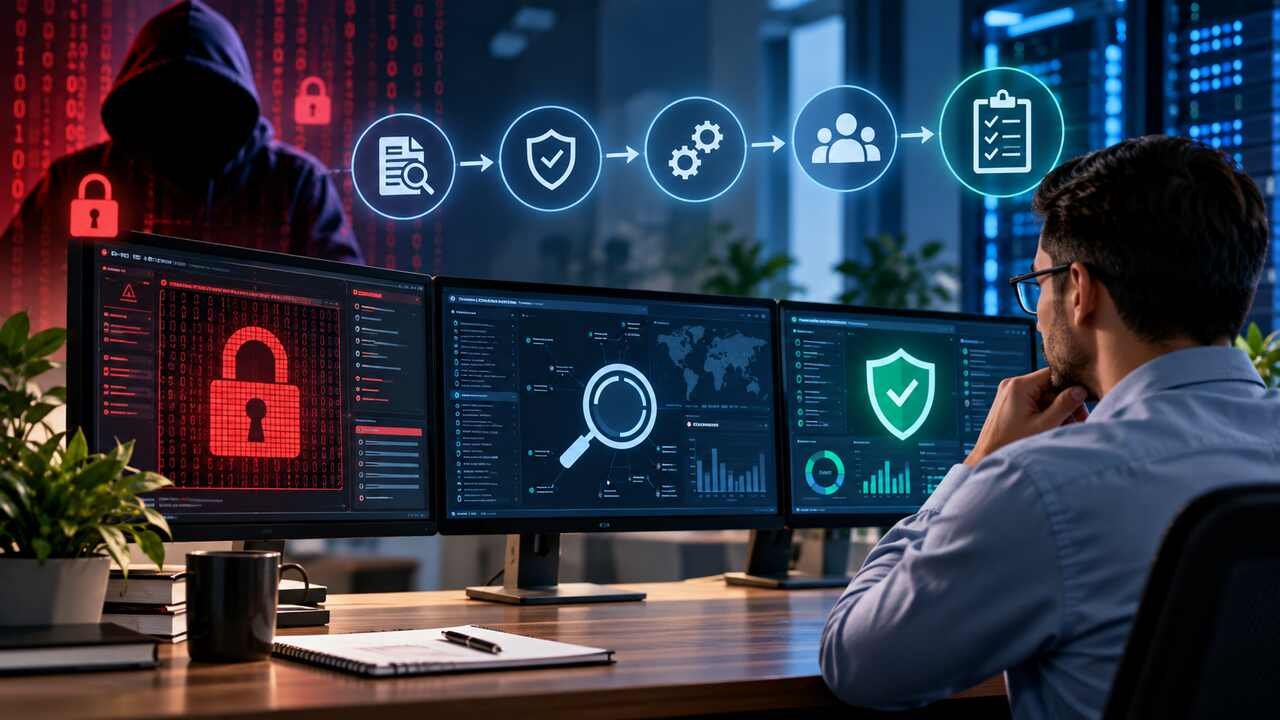
- Record the alert. Capture the user, device, systems involved, time, and observed activity.
- Check for related behavior. Review recent identity, endpoint, network, file, and backup events.
- Contain credible risk. Isolate affected devices or restrict accounts when evidence supports active compromise.
- Protect critical services. Review access to shared storage, privileged systems, and backups.
- Investigate the entry point. Examine phishing, exposed services, stolen credentials, and unpatched software.
- Document decisions. Maintain a clear record for technical leaders, executives, legal teams, and insurers.
- Restore carefully. Recover only after the underlying access path has been addressed.
Each step needs an owner. An alert loses value when responsibility is unclear, especially outside normal business hours.
Preparing for Recovery Before an Alert
Detection and recovery must be planned together. Maintain multiple backup copies in separate locations, protect backup administration accounts, define recovery priorities, and test restoration of important applications. The ransomware risk-management resources from NIST organize ransomware preparation around identifying, protecting, detecting, responding to, and recovering from disruptive events.
A restoration test should confirm more than the return of files. Teams should also validate application settings, permissions, integrations, data freshness, and the ability of users to resume essential work.
Common Ransomware Detection Mistakes
- Relying on one security tool to see every stage of an attack.
- Ignoring identity events because a login appears valid.
- Creating alerts without assigning response ownership.
- Skipping baseline work and treating normal activity as suspicious.
- Protecting production systems but overlooking backup infrastructure.
- Failing to practice account isolation, device containment, and restoration.
Ransomware Detection Priorities
- Connect identity, endpoint, network, cloud, data, and backup signals.
- Set response expectations for high-risk alerts.
- Review privileged access and remote access tools regularly.
- Monitor unusual file changes and data movement.
- Protect backup systems from unauthorized changes.
- Automate repeatable containment steps while retaining human review for complex decisions.
- Test detection and recovery plans at least annually and after major changes.
Final Checklist
- Are unusual logins reviewed quickly?
- Can the team identify rapid file changes and suspicious data movement?
- Are backup systems monitored, protected, and tested?
- Does every high-risk alert have a named owner?
- Can affected accounts and devices be isolated promptly?
- Are clean recovery points available and validated?
Strong ransomware detection is a business process supported by technology. Organizations that combine useful signals, fast decisions, careful access control, protected backups, and tested recovery procedures are better positioned to limit disruption when suspicious activity appears.